0 ratings


商品#:
195806243
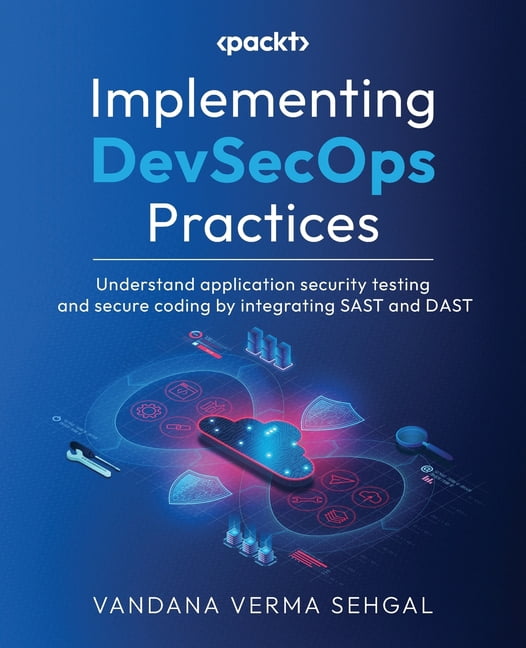
Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST, (Paperback)
商品#:
195806243
TWD 1983
Price Details
Excluding Shipping & Custom charges ( Shipping and custom charges will be calculated on checkout )
*All items will import from 美國
0 ratings
撰寫評論
有存貨
 從USA商店匯入
QTY:
庫存僅剩99件。
立即訂購並活動它 週四, 十月 22
Secured transaction
Ubuy works hard to protect your security and privacy. Our advanced payment security system ensures confidentiality by encrypting your information during transmission using AES (Advanced Encryption Standards) and SSL (Secure Socket Layer) protocols. Your payment details are 100% secure as we do not share your payment details with third party sellers.
Our Top Logistics Partners


Fast
Shipping

Free
Return*

Secure Packaging

100% Original Products

PCI DSS Compliance

ISO 27001 Certified
產品詳情
- Integrate Shift-Left Security, automation, IaC, and compliance into every stage of development, ensuring strong application security and continuous protection for modern software with DevSecOps best practicesKey Features- Understand security posture management to maintain a resilient operational environment- Master DevOps security and blend it with software engineering to create robust security protocols- Adopt the left-shift approach to integrate early-stage security in DevSecOps- Purchase of the print or Kindle book includes a free PDF eBookBook DescriptionDevSecOps is built on the idea that everyone is responsible for security, with the goal of safely distributing security decisions at speed and scale to those who hold the highest level of context. This practice of integrating security into every stage of the development process helps improve both the security and overall quality of the software. This book will help you get to grips with DevSecOps and show you how to implement it, starting with a brief introduction to DevOps, DevSecOps, and their underlying principles.After understanding the principles, you'll dig deeper into different topics concerning application security and secure coding before learning about the secure development lifecycle and how to perform threat modeling properly. You'll also explore a range of tools available for these tasks, as well as best practices for developing secure code and embedding security and policy into your application. Finally, you'll look at automation and infrastructure security with a focus on continuous security testing, infrastructure as code (IaC), protecting DevOps tools, and learning about the software supply chain.By the end of this book, you'll know how to apply application security, safe coding, and DevSecOps practices in your development pipeline to create robust security protocols.What you will learn- Find out how DevSecOps unifies security and DevOps, bridging a significant cybersecurity gap- Discover how CI/CD pipelines can incorporate security checks for automatic vulnerability detection- Understand why threat modeling is indispensable for early vulnerability identification and action- Explore chaos engineering tests to monitor how systems perform in chaotic security scenarios- Find out how SAST pre-checks code and how DAST finds live-app vulnerabilities during runtime- Perform real-time monitoring via observability and its criticality for security managementWho this book is forThis book is for individuals new to DevSecOps and want to implement its practices successfully and efficiently. DevSecOps Engineers, Application Security Engineers, Developers, Pentesters, and Security Analysts will find plenty of useful information in this book. Prior knowledge of the software development process and programming logic is beneficial, but not mandatory.Table of Contents- Introducing DevSecOps- DevSecOps Principles
| Book format | Paperback |
| Fiction/nonfiction | Non-Fiction |
| Genre | Computing & Internet |
| Publication date | December, 2023 |
| Pages | 258 |
| Subgenre | Internet |
| Series title | No Series |
| Edition | 1 |
| Publisher | Packt Publishing |
| Original languages | English |
| Language | English |
| Edu focus | Engineering |
| Is collectible | N |
| Digital file format | |
| Digital reader format | |
| Digital audio file format | |
| Recording time | 0 min |
| Retail packaging | Single Piece |
| Assembled product dimensions (l x w x h) | 7.50 x 0.54 x 9.25 in (19.1 x 1.4 x 23.5 cm) |
| Assembled product weight | 0.99 lb (450 grams) |
| Bisac subject heading | Computers |
產品描述
Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST, (Paperback)
有疑問? 和我們聊天
客戶問題與解答
-
問題:
如何從 Ubuy 在線購物 Implementing DevSecOps Practices: Understand?
Answer: 從 Ubuy 在線購物 Implementing DevSecOps Practices: Understand 非常簡單。. 您只需搜索產品,在結賬時選擇運輸方式,然後將其運送到您所在的位置。 -
問題:
Implementing DevSecOps Practices: Understand 可以在 Taiwan 在線購物嗎?
Answer: 是的,您可以在 Ubuy Taiwan 以合理的價格購買該產品。. Implementing DevSecOps Practices: Understand 在本地不可用,但您可以信任我們的快遞服務。 -
問題:
下訂單後需要多長時間才能收到產品?
Answer: 您訂購的產品的交貨時間根據您訂購的商品和您選擇的運輸方式而有所不同。. 結賬時會提到預計送貨時間,所以購物時請放心。
Vandana Verma Sehgal All Books Editorial Review
未找到編輯評論
Customer Reviews & Ratings
1 客戶評價
-
5 星
100%
-
4 星
0%
-
3 星
0%
-
2 星
0%
-
1 星
0%
評論這個產品
和其他客戶分享您的想法
Product Price History
重要資訊
- 限制:對於國際運輸的產品,請注意任何製造商保修可能無效;製造商服務選項可能不可用;產品手冊、說明和安全警告可能不是目的地國家的語言;產品(及隨附材料)的設計可能不符合目的地國家的標準、規範和標籤要求;並且產品可能不符合目的地國家的電壓和其他電氣標準(如果適用,需要使用適配器或轉換器)。收件人有責任確保產品可以合法進口到目的地國家。當從Ubuy或其關聯公司訂購時,收件人是記錄在案的進口人,並且必須遵守目的地國家的所有法律和法規。
- 由於Ubuy是一個全球搜索引擎,因此並非Ubuy上列出的所有產品都在出售。產品受出口/貿易法規的約束。
TWD 1983
立即訂購並活動它 週四, 十月 22
This item is not restrict in my country.(Please click on above link if this item is not restrict in your country, So our team will review and allow.)
QTY:
庫存僅剩99件。
Secured transaction
PCI DSS compliant and ISO 27001:2022 certified, with encrypted payments and full buyer protection on every order.
Our Top Logistics Partners
Fastest cross-border delivery
Ubuy Assurance
Experience worry-free shopping with 100% original products, PCI DSS-compliant payment security, ISO 27001-certified data protection, the fastest cross-border delivery, free returns *, and secure packaging on every order.